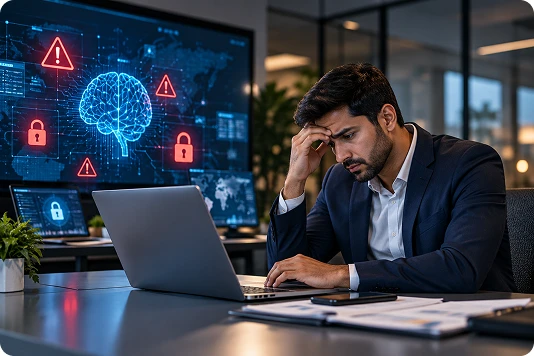
Your business runs on AI. But does your AI run securely? Agentic India delivers end-to-end AI security services, from AI cybersecurity consulting and LLM security to generative AI threat detection, AI model security, and agentic AI security. We protect your AI infrastructure, training data, autonomous agents, and AI-powered workflows from prompt injection, model poisoning, adversarial attacks, and unauthorized access.
Traditional cybersecurity was built for fixed perimeters and known threat signatures. It was not built for large language models manipulated through prompt injection, AI models poisoned during training, autonomous agents that make decisions with real-world consequences, or generative AI outputs that silently leak proprietary data into uncontrolled external systems. If your organization is deploying AI and relying on generic security controls, your exposure is growing faster than your protection.
Every service we offer is designed from the ground up for AI-native risk. We do not apply legacy cybersecurity controls to AI systems and call it AI security. We build protection that understands how LLMs, generative AI systems, and autonomous agentic workflows actually work and, more importantly, where they actually fail under attack.
Assess your AI environment, identify gaps in model governance, data handling and access controls, and get a ranked remediation roadmap aligned with NIST AI RMF, ISO 42001 and OWASP LLM Top 10.
AI-native monitoring to identify anomalous behavior, unauthorized access and adversarial inputs in real time, with sub-second alerting and pre-built response playbooks.
Protect datasets, embeddings and vector databases with data minimization, differential privacy techniques and access governance that meets GDPR, HIPAA and India's DPDP Act requirements.
Harden your AI models against adversarial attacks, data poisoning, model inversion and model extraction. Coverage for proprietary and open-source models, across any cloud or on-premises infrastructure.
Map AI operations to EU AI Act, NIST AI RMF, ISO 42001, SOC 2 and OWASP LLM Top 10. Produce audit-ready documentation and support your compliance teams through regulatory review cycles from assessment to sign-off.
Implement prompt injection defenses, output filtering, input sanitization and access controls for LLMs in customer-facing and internal applications. Security built in from the first architecture decision.
Simulate adversarial attacks on your AI systems, including jailbreaks, prompt injection chains, model extraction and multi-step agent manipulation. We test the way attackers think.
Secure multi-agent systems and autonomous workflows with agent boundary controls, tool-use restrictions, memory governance and real-time behavioral monitoring.
Deploy real-time output guardrails that prevent harmful, biased or non-compliant responses, protecting your users, brand and regulatory standing without disrupting legitimate operations or degrading user experience.
AI security is not a single point of control. It is a layered program addressing different attack surfaces across your AI environment. Here is how each service works and what it specifically delivers for your organization.
Continuous visibility into every AI asset in your organization, from approved enterprise tools to shadow AI discovered in employee workflows. We inventory, risk-score, and monitor your AI posture continuously so your security team always knows what AI is running, who is using it, and what data it is accessing.
Every engagement starts with a real business problem. These are three outcomes Agentic India delivered for clients in healthcare, retail, and customer support, drawn directly from our case studies portfolio.
Ready to Secure Your AI Systems?
Talk to our AI security experts about your models, data, and agentic workflows.
Talk to Our AI Security ExpertsYour AI systems are only as trustworthy as security controls protecting them. A well-designed AI security program delivers measurable outcomes across risk reduction, regulatory compliance, operational continuity, and board-level confidence that generic security programs simply cannot match.
We follow a structured delivery process that moves from business discovery through to deployed, continuously monitored AI security controls. Each stage has defined deliverables and technical checkpoints before the next phase begins, so you always know exactly where your program stands.
We map every AI asset in your environment: models in production, data pipelines, API integrations, third-party tools, and shadow AI in active employee use. We score your current posture against NIST AI RMF and OWASP LLM Top 10 and deliver a gap analysis report. Typical delivery: 2 to 3 weeks.
We build an AI-specific threat model for your environment, documenting attack surfaces, adversarial scenarios, and risk priorities in the context of the specific AI architectures you actually run. We go beyond generic frameworks and map threats to your real production systems.
We implement technical controls at the model layer: adversarial robustness training, access controls, inference monitoring, and input/output sanitization. For LLMs and generative AI, we configure prompt security layers and content moderation pipelines matched to your use case.
We deploy monitoring agents, behavioral baselines, and real-time guardrails across your AI systems. Automated alerting and response playbooks ensure your team can act in minutes, not hours, when anomalies, adversarial inputs, or policy violations are detected in production.
We map your implemented security controls to every applicable regulatory framework, produce audit-ready documentation, and support your compliance and legal teams through regulatory review cycles from initial gap identification through to final documentation sign-off.
AI threats evolve as your systems scale and as attacker techniques improve. Our managed monitoring service provides continuous visibility into your AI security posture, monthly reporting, threat intelligence updates, and proactive model re-hardening as your AI environment changes.
AI security is not a single control point. It applies across every layer of your AI architecture, from the models themselves and the data they access to the agents that operate them, the infrastructure that hosts them, and the third-party tools your teams use without IT approval.
Customer-facing chatbots, internal knowledge assistants, document analysis systems, and AI-powered search built on GPT, Claude, Llama, Gemini, Mistral, or any other foundation model deployed in production.
Training data ingestion, model training, evaluation, and deployment pipelines where data poisoning and model tampering risks are highest and, in most organizations, least monitored by any security control.
AI workloads running on AWS, Azure, GCP, or private cloud, including model inference API endpoints, model serving infrastructure, and the data storage layers holding your training and fine-tuning assets.
Autonomous AI agents that call external APIs, execute code, access databases, browse the web, and make real-world decisions across multi-step tasks, including complex multi-agent orchestration architectures.
Open-source models, vendor AI APIs, and AI features embedded in SaaS products your teams are already using, including tools adopted without IT awareness or approval and flagged through shadow AI discovery.
Vector databases, embedding stores, training datasets, fine-tuning datasets, and retrieval-augmented generation knowledge bases that hold your most strategically sensitive and competitively valuable organizational data.
We work with the leading tools across LLM security, AI posture management, threat detection, red teaming, data privacy, and AI governance. Our technology selection is always driven by your existing environment and your specific AI architecture, not by vendor relationships or preferred tooling.
Most organizations discover too late that their existing cybersecurity vendor does not actually understand AI. They apply network and endpoint security thinking to AI systems and miss the attack surfaces that matter most. Here is where the difference shows up in a direct comparison that goes beyond marketing claims.
| Capability | Traditional Security Vendors | Agentic India |
|---|---|---|
| AI system expertise | Generic IT security retrofitted for AI as an afterthought |
Built natively for LLMs, generative AI, and agentic architectures |
| Agentic AI coverage | Absent from most security frameworks and service offerings |
Full multi-agent and autonomous workflow security included as standard |
| Shadow AI discovery | Rarely covered or limited to basic network traffic detection only |
Continuous AI asset discovery and posture management included |
| LLM-specific testing | Prompt injection and jailbreak testing not in scope or capability |
Full LLM attack surface testing standard across all engagements |
| OWASP LLM Top 10 | Alignment uncommon, rarely part of any engagement deliverable |
Built into every LLM and generative AI security engagement |
| Compliance frameworks | GDPR and ISO 27001 coverage only |
NIST AI RMF, EU AI Act, ISO 42001, OWASP LLM Top 10, plus sector frameworks |
| Speed to protection | 3 to 6 months before meaningful AI-specific controls are in place |
Security-ready within 4 to 6 weeks of engagement commencement |
| AI supply chain security | Third-party model vetting not a covered service |
Full supply chain vetting including open-source model integrity assessment |
Our team comes from AI development, not from traditional cybersecurity retrofitted for AI. We understand what makes LLMs, generative AI systems, and autonomous agentic workflows fundamentally different from conventional software: non-deterministic outputs, emergent behavior, multi-step reasoning chains, dynamic tool use, and training pipelines.
We specialize in securing autonomous AI agents and multi-agent systems. Conventional security providers do not. Our engineers have built and secured agentic AI systems in production environments across multiple industries.
We do not offer AI security as one line item in a catalog of 50 services. It is what we do. Every engineer working on your engagement is focused on AI security exclusively, not splitting attention across network monitoring, endpoint management.
AI security requirements vary significantly by sector, driven by the sensitivity of the data AI systems handle, the regulatory frameworks governing their use, and the business-critical nature of the decisions they support.
Secure AI-powered fraud detection, credit scoring, and customer service systems against adversarial manipulation and model theft. Compliance coverage for RBI, SEBI, GDPR, and DPDP Act requirements built into every engagement.
Protect clinical AI systems, diagnostic models, and patient data pipelines with HIPAA-aligned controls and shadow AI governance that satisfies both regulators and clinical risk officers across distributed healthcare environments.
Secure AI recommendation engines, dynamic pricing systems, and inventory automation against data poisoning and adversarial manipulation.
Harden AI systems in predictive maintenance, quality control, and supply chain automation against adversarial sensor manipulation and industrial espionage targeting the proprietary process data that these systems depend on.
Secure AI document review and contract analysis systems against data leakage, unauthorized access to privileged materials, and adversarial manipulation of legal reasoning outputs that could affect case outcomes and professional liability.
Protect AI tutoring, assessment, and content generation platforms from prompt injection, data leakage, and bias exploitation, ensuring the safety and integrity of AI tools used by students and educators at every level.
Secure AI systems in public service delivery, fraud detection, and public safety applications with the strictest available access controls, adversarial robustness standards, and audit documentation requirements.
Protect AI-driven network optimization, fraud detection, and customer experience systems from adversarial attacks that exploit real-time inference at the high query frequencies that production telecom AI systems operate continuously.
We offer three engagement models designed to match different organizational needs, risk profiles, and budget structures, from a focused one-time audit to a fully managed ongoing AI security program that operates as an extension of your team.
A defined-scope AI security engagement with clear deliverables, timelines, and documented outcomes. Suited for organizations conducting a first-time AI security audit, an LLM security assessment ahead of a product launch, or an AI red teaming exercise before a major deployment.
Continuous AI security coverage on a monthly retainer basis. Includes regular posture reviews, threat intelligence updates, model monitoring, and compliance reporting. For organizations where AI is core to their product or operations and continuous visibility is a non-negotiable requirement.
Dedicated AI security engineers embedded with your product or engineering team for organizations building AI at scale. We operate as an extension of your team, securing AI systems from architecture design through production deployment and continuous operation.
Cybersecurity protects networks, endpoints, and data from known attack classes. AI security specifically addresses the threats that arise from AI systems themselves: prompt injection, model poisoning, adversarial inputs, training data leakage, model theft, and the unpredictable behavior of autonomous AI agents executing multi-step tasks.
A foundational AI security audit covering model inventory, posture assessment, and NIST AI RMF gap analysis typically takes 2 to 3 weeks. A full implementation of security controls across a production AI environment typically takes 4 to 8 weeks depending on the number of AI systems in scope, the complexity of your AI architecture, and the regulatory frameworks you are aligning to.
Yes. We secure AI applications built on any foundation model, including OpenAI GPT, Anthropic Claude, Google Gemini, Meta Llama, Mistral, Cohere Command R, and any open-source model deployed in your infrastructure. Our controls operate at the application layer, the API integration layer, and the data layer, independently of which underlying model provider you use.
We align AI security programs with NIST AI RMF, EU AI Act, ISO 42001, ISO 27001, OWASP LLM Top 10, SOC 2 Type II, GDPR, HIPAA, and India's DPDP Act. We also support clients preparing RBI and SEBI AI governance requirements and for sector-specific AI regulatory requirements in healthcare, financial services, and government.
Yes. Most enterprise clients transition to a managed AI security services model after the initial implementation is complete. This provides continuous monitoring of your AI systems, monthly security posture reviews, proactive model re-hardening as your systems and data evolve, and ongoing compliance reporting.
Agentic AI security addresses the unique risks of autonomous AI systems that plan, reason, call external tools, and execute multi-step tasks with real-world consequences. These systems have attack surfaces that have no equivalent in conventional software: tool-use manipulation, agent-to-agent prompt injection, memory poisoning, and cascading failure across multi-agent pipelines.